RunSafe Security’s CEO Joe Saunders recently hosted a panel discussion on Monitoring Open-Source Software in SAAS Infrastructure. His panel included innovative business leaders in the software, technology, and security sectors: Jonathan B Fishbeck, Founder and...
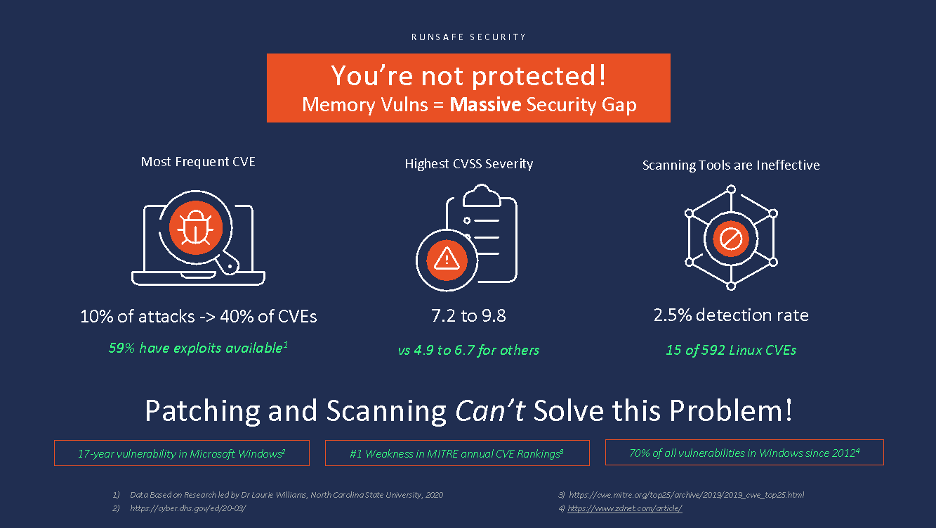
Current strategies of scanning for and patching vulnerabilities in software leave a huge and highly-exploitable security gap. Recent research by RunSafe Security partners show that current strategies of scanning for and patching vulnerabilities in software leave a...
-It’s not always enough to just be safe, sometimes you need to be fast too. RunSafe is in the business of helping developers – and the organizations that employ them – to reduce risk. A key part of purpose is making sure our customers have the right...
With the release of “Lessons from the School of Cyber Hard Knocks” podcast, I have been reminded of the importance of learning from our mistakes as a core pillar of our company culture at RunSafe Security. Through internal training sessions, every employee takes a...
In July 2020 the Atlantic Council, a highly-respected international affairs leadership institute based in Washington, DC, published a wide-ranging, evidence-based report titled “Breaking Trust: Shades of Crisis Across an Insecure Software Supply Chain” from its...
This post, by Nick Rea, RunSafe Security’s VP, Market Development, originally appeared on the Oracle Cloud Infrastructure Blog: Managing cybersecurity vulnerabilities for organizations of any size is no small task. For organizations that produce their own code,...