SBOMs for Embedded Systems: Solving the C/C++ Visibility Problem

SBOMs are essential for compliance and security, but C/C++ embedded projects make them notoriously difficult to generate. See how RunSafe solves the challenge—fast, accurate, and CI/CD-ready.

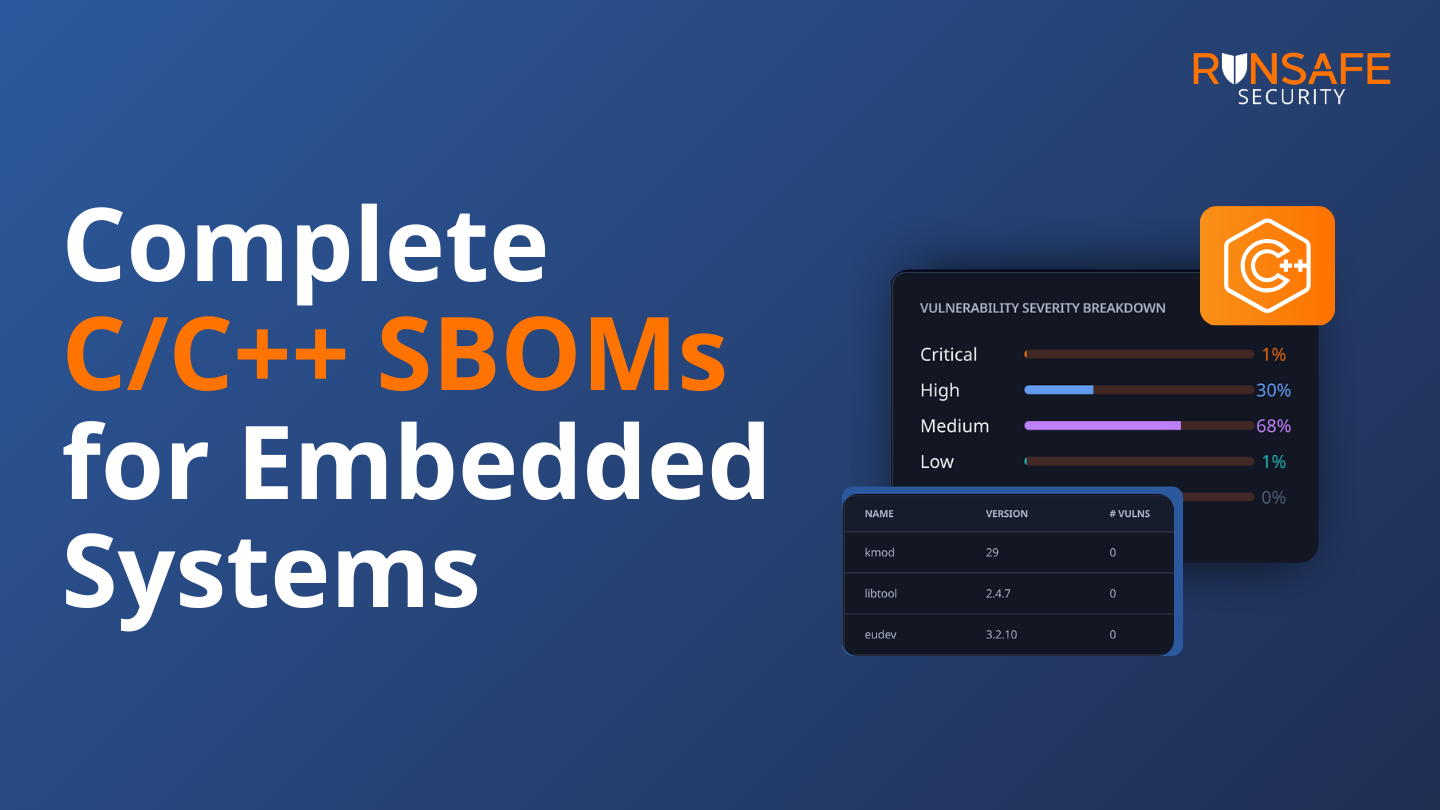
Complete C/C++ SBOMs for Embedded Systems

Generate Complete C/C++ SBOMs Without the Headaches

Software Bills of Materials (SBOMs) are now a critical requirement for software security and regulatory compliance. But for C and C++—especially in embedded systems—hidden dependencies, legacy code, and opaque build artifacts can leave dangerous blind spots.

In just 60 seconds, discover how RunSafe Security eliminates these challenges. Our platform captures complete, exportable SBOMs for C/C++ without requiring a package manager. Integrated directly into your CI/CD pipeline, our solution delivers accurate dependency mapping, vulnerability insights, and the clarity you need to secure your software supply chain.

CRA Readiness: Build an SBOM You Can Act On

CRA Readiness: Build an SBOM You Can Act On

Under the Cyber Resilience Act, having an SBOM is only the beginning. Manufacturers need to know exactly what software is in each product release and be able to quickly determine which products are affected when a new vulnerability emerges. For embedded software, that...

read more
Operational Software Assurance

Operational Software Assurance

Security Cannot Stop When Software Ships Critical software can remain deployed for years or even decades. During that time, new vulnerabilities emerge, threats evolve, and AI is accelerating both vulnerability discovery and exploit development. But patching, testing,...

read more