Inside RunSafe: A Quick Look at Our Mission, Platform, and Impact
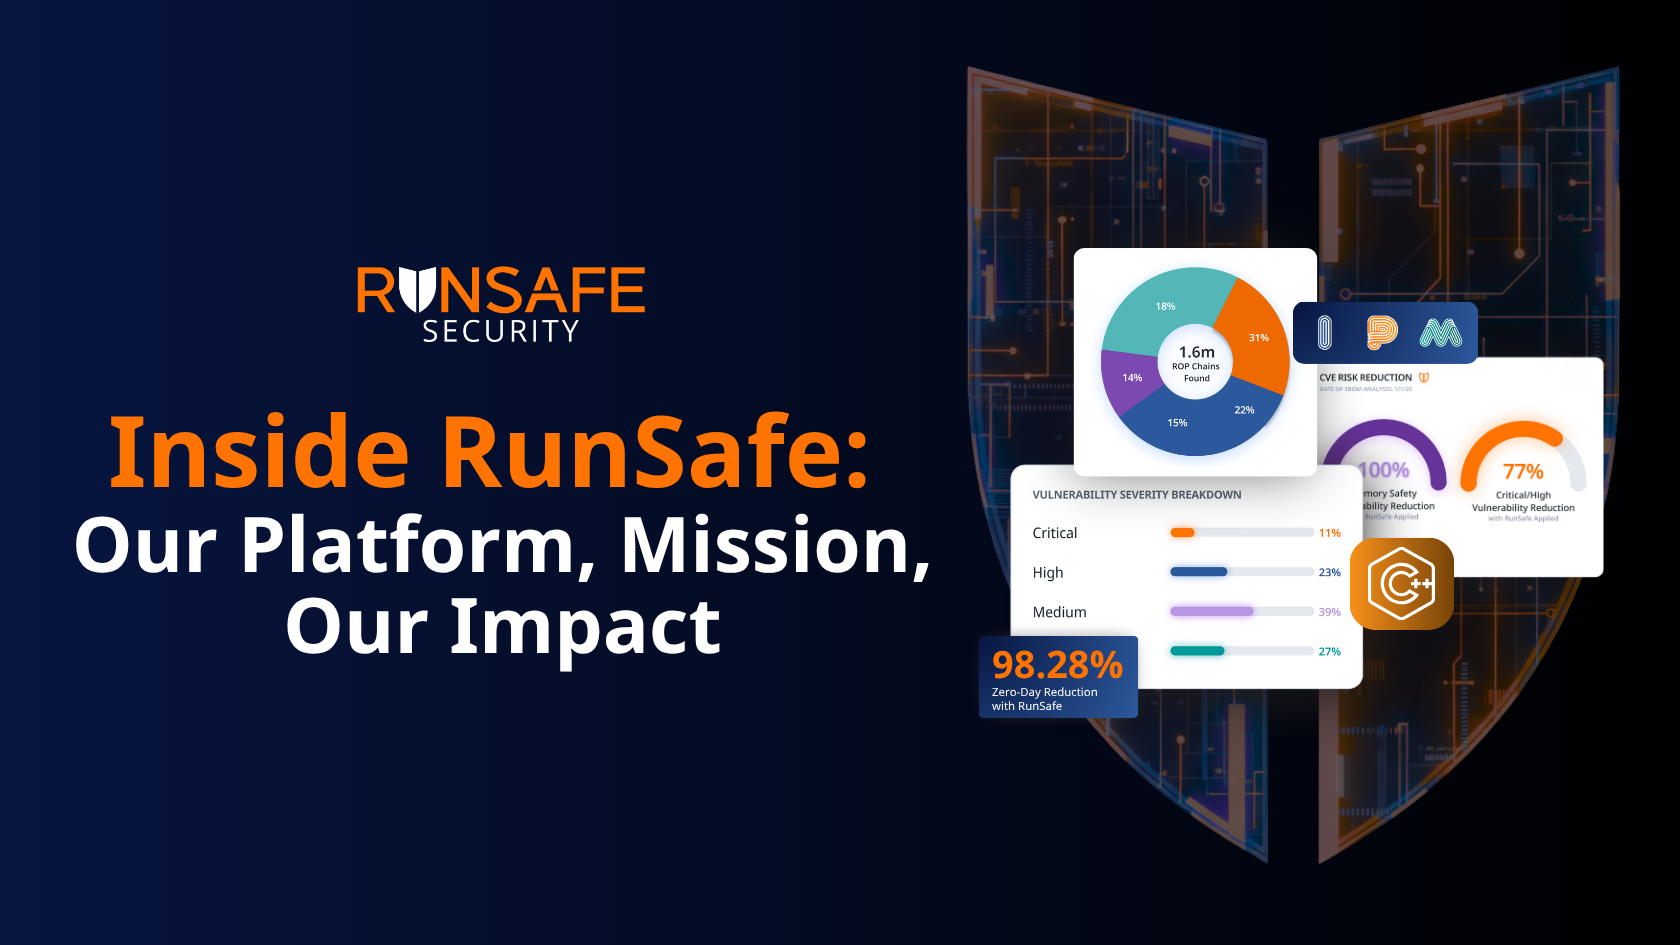
RunSafe Security is dedicated to protecting the world’s most critical software across defense, infrastructure, automotive, and medical systems. In this video, you’ll see how our platform delivers a secure-by-design approach that stops vulnerabilities before they can be exploited. From identifying hidden risks and generating Software Bills of Materials (SBOMs) to hardening software at build-time and runtime, RunSafe ensures that critical systems remain resilient, reliable, and secure. By integrating our Identify, Protect, and Monitor capabilities, we give organizations the tools to proactively defend against attacks across the entire software supply chain.
Our mission is clear: neutralize the vulnerabilities attackers rely on, enabling safe and uninterrupted operations across industries where security and reliability are non-negotiable. RunSafe’s platform not only automates embedded security but also provides real-time visibility into software health, helping teams maintain strong security posture without slowing innovation. Trusted by organizations around the globe, RunSafe proves that comprehensive cybersecurity can be both powerful and seamless—making every system, every product, and every mission more resilient.